




New Delhi: There is so much phishing campaign, which is for hacker for the innocent users, to get their almost personal details like the bank accounts and their personal id of their social media, but this time there is also an latest phishing campaign targeting Gmail users through a multi-layered attack that uses legitimate Microsoft Dynamics infrastructure to bypass security measures and steal login credentials. The attack begins with the deceptive New Voice Notification emails that appear to come from legitimate voicemail services. These emails contain spoofed sender information and the prominent Listen to Voicemail buttons that redirect victims through a complex chain of compromised websites.
This phishing operation employs a particularly clever initial vector, using Microsoft’s legitimate Dynamics marketing platforms to host the first stage of the attack. This technique provides immediate credibility and helps evade email security filters that typically flag suspicious domains. After clicking the malicious link, victims are redirected to a CAPTCHA page hosted on the horkyrom[.]com, a domain registered in Pakistan. The CAPTCHA serves as a trust-building mechanism, creating the illusion of legitimate security measures while actually being part of the attack.
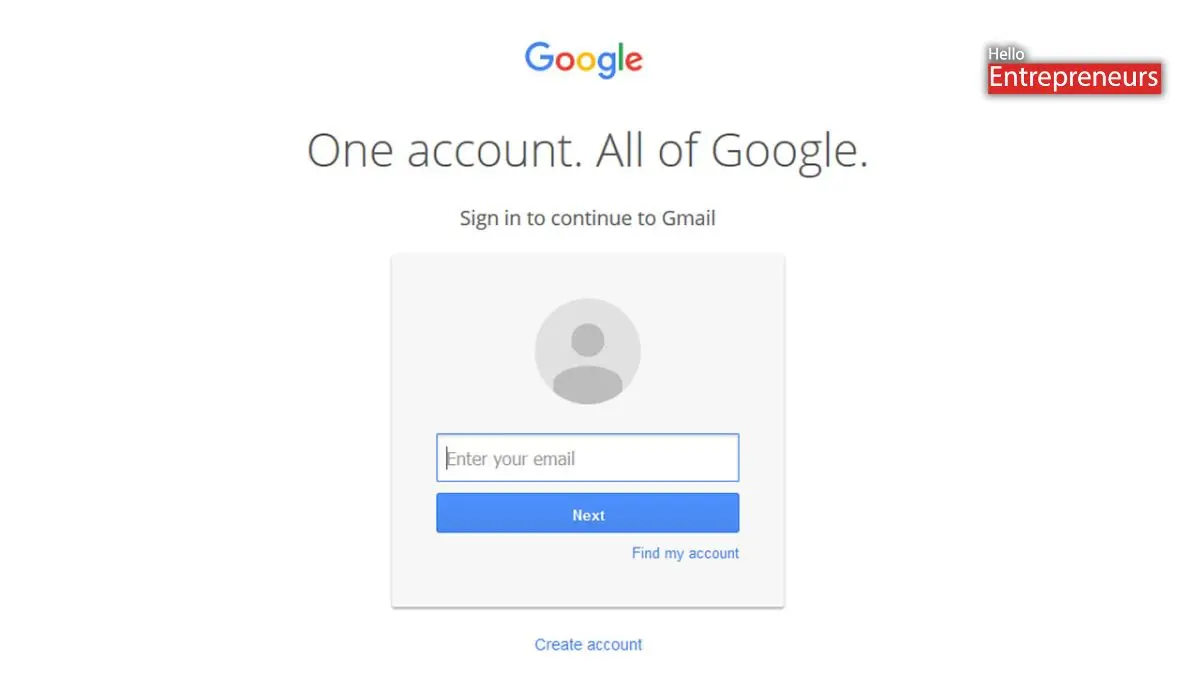
The final stage presents users with the pixel-perfect replica of Gmail’s login page, complete with the Google branding and authentic-looking interface elements. The fake login form captures both primary credentials and advanced security measures, including two-factor authentication codes, backup codes, and security questions. The attack also leverages multiple redirection layers and cross-site requests to servers in Russia, indicating a complex international infrastructure designed to evade detection and complicate forensic analysis. Those stolen credentials are immediately transmitted to attacker-controlled servers, allowing for the rapid compromise before victims realize they have been targeted.
Security teams are advised to block this domain and monitor for similar campaigns using the legitimate marketing platforms as initial compromise vectors. Users who believe they may have been targeted should immediately change their Google account passwords and review recent account activity.