



Surat: Protecting personal information collected through digital means has become extremely necessary in today’s times, where the rights of data principals, data fiduciaries (organizations that collect and process data) as well as special categories like banks and large corporations as significant data fiduciaries. Additional responsibilities apply to organizations falling under this category.
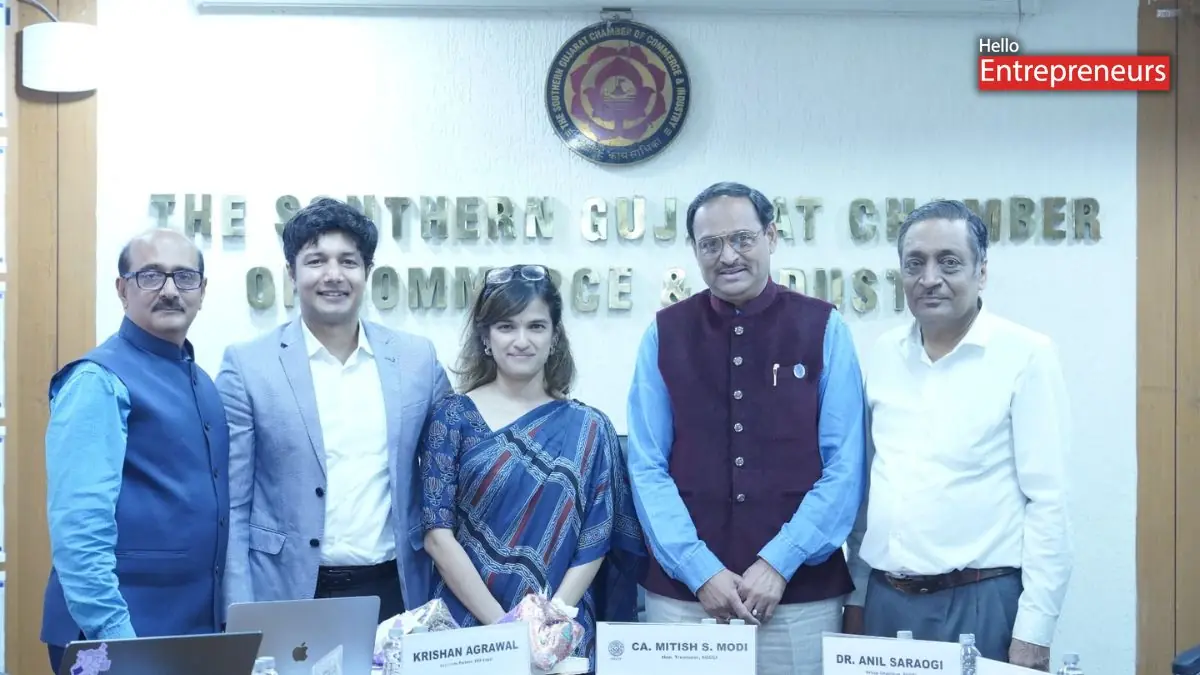
This was revealed by Krishna Agarwal, associate partner of SRA Legal and Sporta Technologies private limited who provided the detailed guidance at the awareness and training workshop on ‘Digital Personal Data Protection Act 2023’ organised by the Southern Gujarat Chamber of Commerce and Industry (SGCCI).
CA Mitish Modi said the Digital India Platform and data is the main source for it too. Data is confidential, transparent and impartial, hence its importance increases a lot. With the implementation of the Digital Personal Data Protection Act, 2023, understanding and compliance with the data protection law has become mandatory for every industry and organization.
Agarwal explained in detail about the Data Protection Board and said that the Data Protection Board is an enforcement and regulatory authority, which is empowered to impose penalties for violations of the law. There are heavy penalty provisions under the law, so it is imperative for organizations to comply with the rules.
He also gave guidance on practical measures to be adopted by organizations such as preparing a data protection policy, strengthening internal control systems, implementing data security mechanisms and ensuring timely compliance, along with the penalty provisions. He urged entrepreneurs to implement the necessary policies and procedures in a timely manner.
Ritika Das, Senior Legal Manager, Sporta Technologies Pvt. Ltd., provided guidance on data governance, internal controls and risk management at the corporate level. She explained through practical case studies that organizations managing personal information on digital platforms need to prioritize transparency and security.
She explained through examples of practical case studies that no company or organization can collect unnecessary personal information. While collecting data, it is necessary to adopt the principle of minimum necessary data. That is, only as much clear and relevant data as is required for the product or service should be collected. Along with this, citizens should also refrain from providing unnecessary personal information.
Das said that some companies indicate consent by ticking a tick mark in an online form or check box in advance, which is not the right method. Consent must be clear, voluntary and informed. No company or organization can force an individual to provide personal data. He further said that data security is not only a legal obligation but also a moral responsibility of the organization. Only by adopting proper data management practices can the trust of the customers be maintained.